Security Incident on Realms: Malware in Plugin Files (October 2026)
We found malware in the plugin files of our Realms server. Here is what happened, which data may be affected, and what we have done about it.
 Sen
On 17 October 2026 we found malware inside the plugin files of our Realms server. It hid in plugins that still worked normally, quietly downloaded an extra program from the attacker's server, and ran it inside Realms.
We want to explain openly what happened, which data may have been taken, and what we have done. This notice is also part of our obligations under Indonesia's Law No. 27 of 2022 on Personal Data Protection (UU PDP).
What Happened?
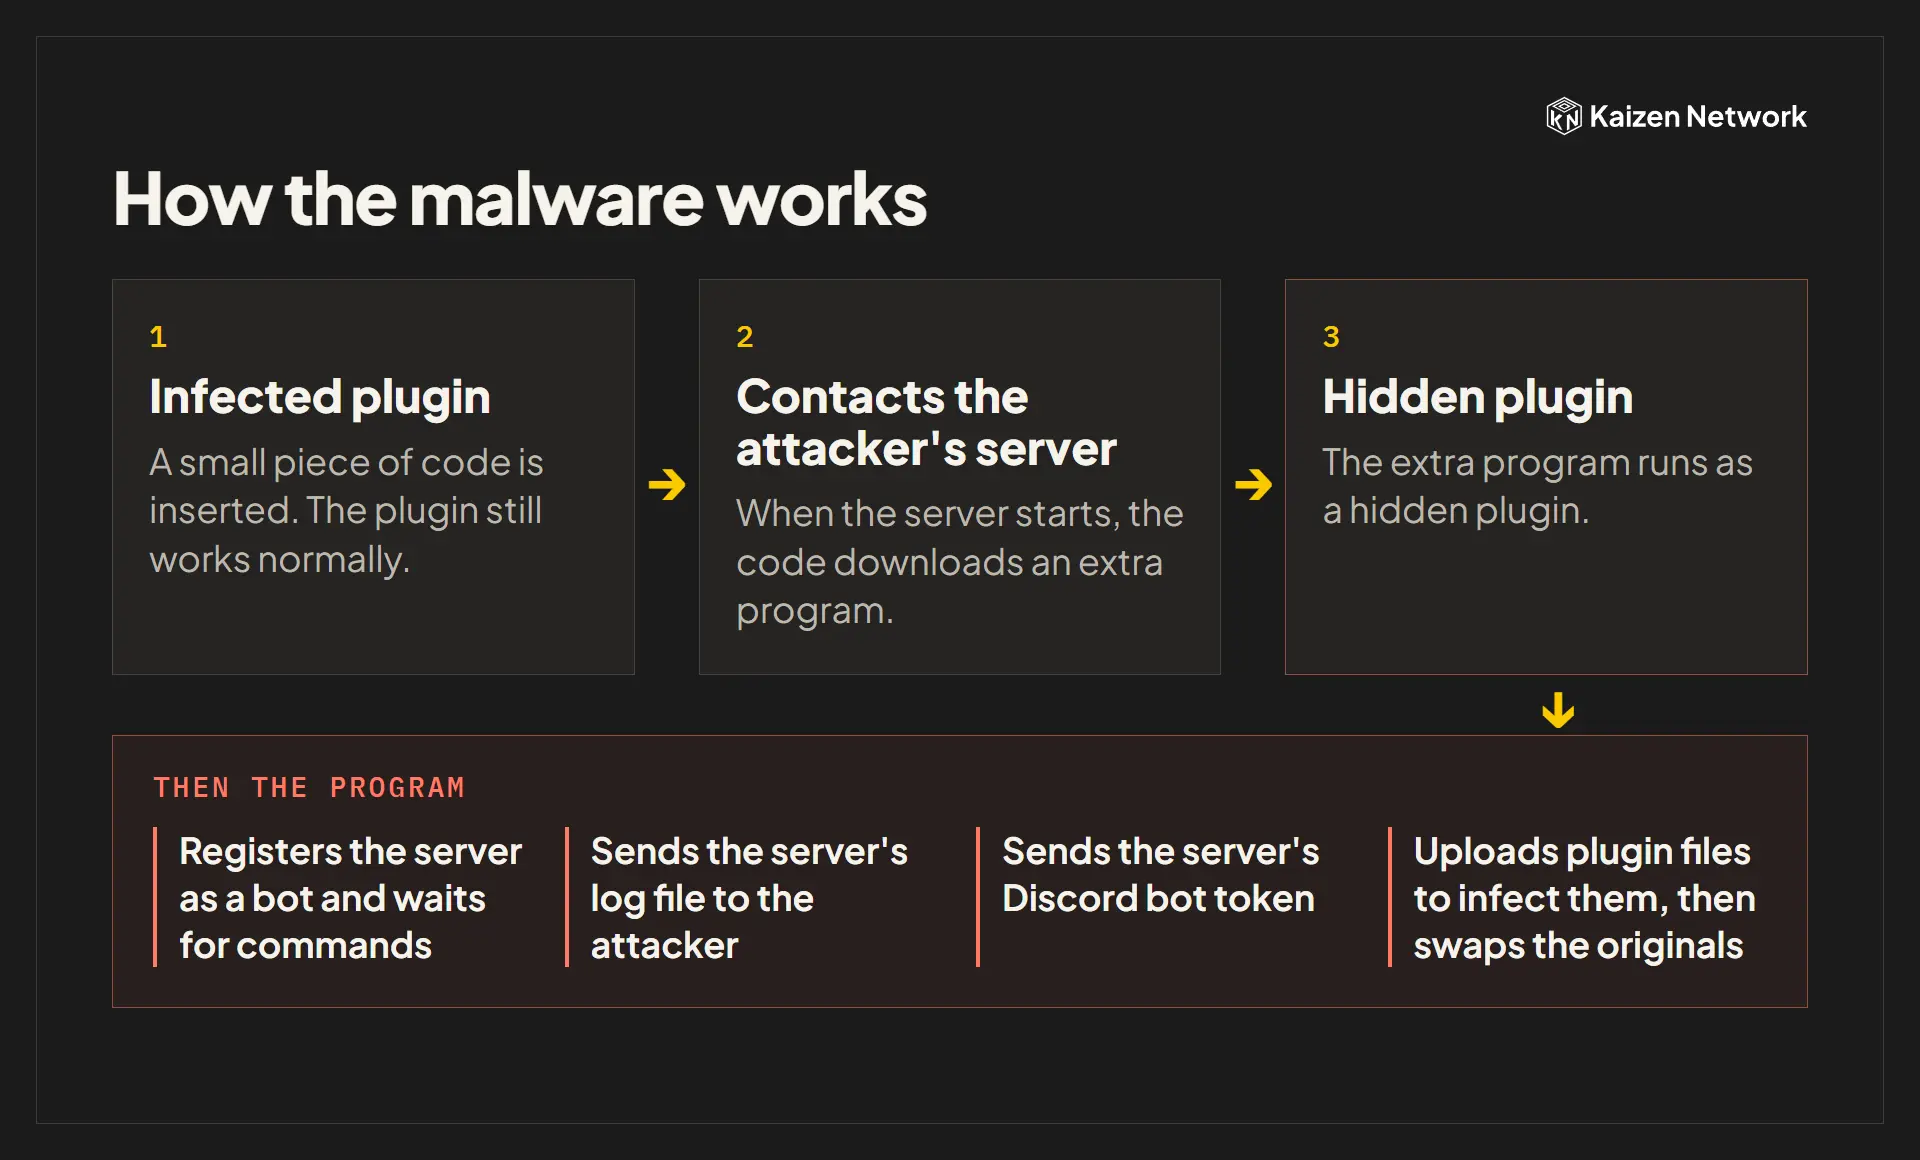
The malware inserts a small piece of code into plugin files without changing how the plugin behaves. When the server starts, that code contacts the attacker's server, downloads an extra program, and runs it as a hidden plugin.
From our analysis on a separate, isolated machine, the extra program:
- registers the server as a "bot" and waits for commands from the attacker,
- sends the server's log file to the attacker,
- sends the server's Discord bot token,
- uploads plugin files to the attacker's server to infect them. From what we found on Realms, the originals are then swapped for the infected copies.
The malware was only found on Realms. We checked the plugin files and main server files of every other server on Kaizen Network (Lobby, Survival Mix, Tycoon, Creative), and none of them were infected.
We have not been able to confirm how the malware first got into Realms. What we know is that it had been on Realms since at least 30 May 2026.
Short Timeline (WIB, UTC+7)
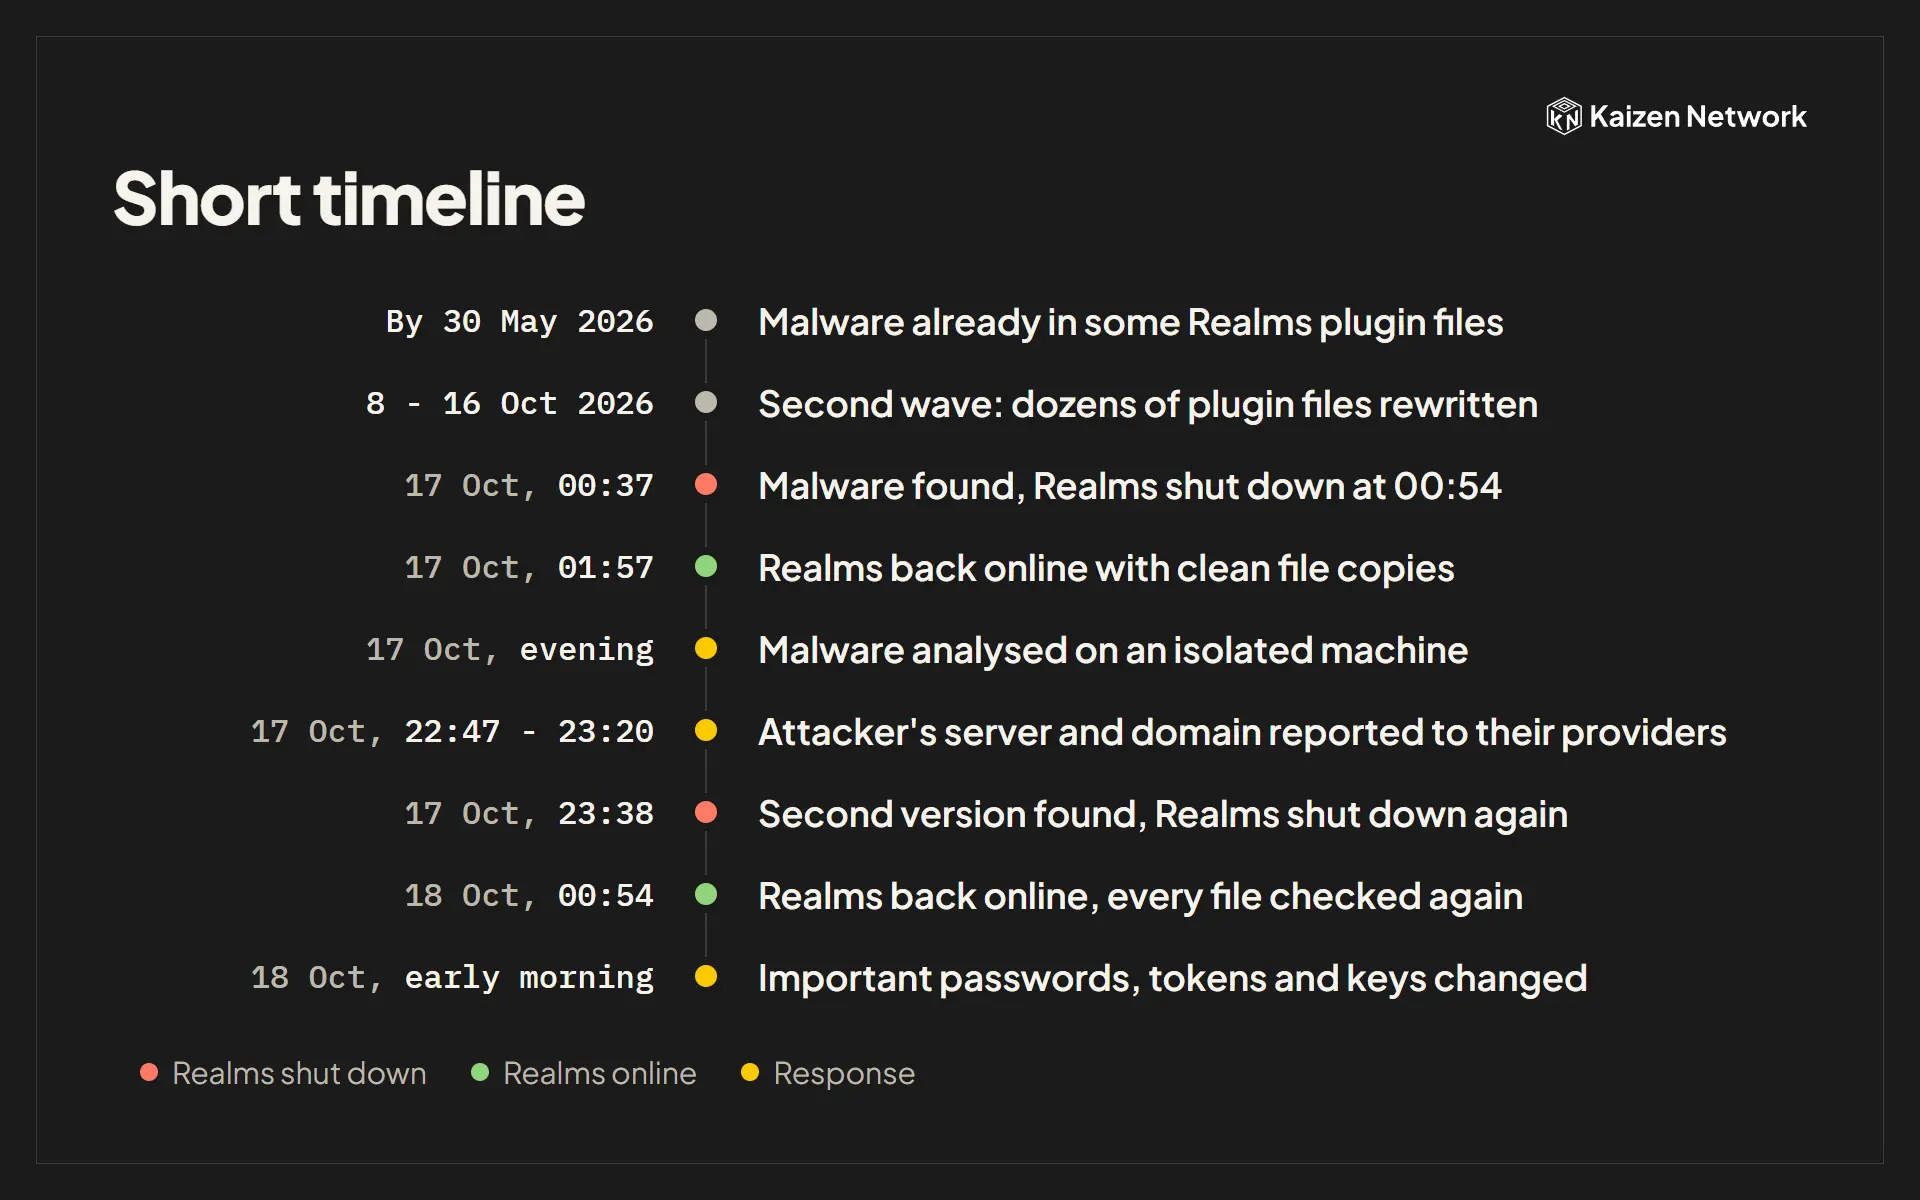
| Time (WIB) | Event |
|---|---|
| By 30 May 2026 | Malware already present in some Realms plugin files (found later from old file copies). |
| 8 - 16 Oct 2026 | Second wave: dozens of Realms plugin files rewritten by the malware. |
| 17 Oct, 00:37 | Malware found. We shut Realms down at 00:54. |
| 17 Oct, 01:57 | Realms back online after the infected files were replaced with clean copies. |
| 17 Oct, evening | Malware analysed on an isolated machine. In our test, it sent server logs and the Discord bot token to the attacker's server. |
| 17 Oct, 22:47 - 23:20 | The attacker's server and domain reported to their domain registrar, hosting provider and DNS provider. |
| 17 Oct, 23:38 | We found a second version of the malware that the first cleanup missed, still active since 01:57. Realms shut down again. |
| 18 Oct, 00:54 | Realms back online after every file was replaced or cleaned and checked again. |
| 18 Oct, early morning | The important passwords, tokens and keys that Realms could read were changed. |
Which Data May Be Affected?
We cannot yet confirm exactly which data was taken, because there is no record of network traffic from Realms. Based on how the malware behaved in our analysis, this is our assessment:
| Data | Status |
|---|---|
| Realms server logs: Minecraft usernames, UUIDs, IP addresses when joining Realms, and chat messages and commands typed on Realms | Most likely taken. The malware sends this log file automatically. |
| Realms game data (in-game bank balances, auctions, play statistics) | Unknown. The malware could read the database passwords, but there is no evidence that these databases were accessed. All of those passwords have been changed. |
| Links between Discord and Minecraft accounts (network-wide, not only Realms) | Unknown. The malware could read the database password, but there is no evidence that this database was accessed. The password has been changed. |
| Kaizen Network Discord server: channels the Realms bot could read | Unknown. The bot token was taken, so it could be used to read channels or send DMs as the bot until we changed it on 18 October. There is no evidence that it was misused. |
| Kaizen Network account passwords (server and website login) | Not affected. They are not stored on Realms. |
| Payment data and Premium Points | Not affected. Realms holds no payment data. |
| Players who only played on other servers | No sign of impact, apart from the Discord account links above. |
Affected players are those who joined Realms up to 17 October 2026 (the malware was there by 30 May 2026), plus players who linked their Discord and Minecraft accounts.
The main risk: usernames and IP addresses can be used for scams aimed at players, or to estimate a rough location (such as a city).
What We Have Done
- Shut Realms down as soon as the malware was found, and again when the second version was found.
- Replaced every infected file, including the main server file, with official copies or verified clean copies. Paid plugins without a clean copy were cleaned by removing exactly the part the malware had inserted.
- Re-checked every file on Realms before and after starting the server, and checked the plugin files and main server files of every other server on the network.
- Changed the important credentials Realms could read: the Discord bot token, database passwords, access keys and the security token shared between servers.
- Reported the attacker's domain and server to their registrar, hosting provider and DNS provider so they can be taken down.
- Wrote a technical report for other server owners so they can check their own servers.
What Should You Do?
Nothing is required. Your Kaizen Network password is not affected. Still, we recommend:
- Be careful with messages (including DMs from bots) claiming to be from Kaizen Network staff, especially ones that mention your Minecraft name or your activity on Realms and then ask for a password, a code or a download. Our staff never ask for passwords.
- Do not download "plugins", "mods" or "clients" from people you do not know. This kind of malware spreads through plugin files.
- If you also run your own Minecraft server, read our technical report on how to check it.
Contact
If you have questions about your personal data in connection with this incident, contact us at [email protected]. The data controller for this service is PT Kaizen Network Indonesia. We will update this page if we learn more.
We are sorry this happened. Protecting player data is our responsibility, and we are tightening how we check every file that goes onto our servers.
Summary
| Aspect | Detail |
|---|---|
| What | Malware in the plugin files of the Realms server |
| Since | By 30 May 2026; found 17 October 2026 |
| Affected | Only the Realms server was infected |
| Data most likely taken | Usernames, UUIDs, IP addresses, chat and commands from the Realms server logs |
| Unknown | Realms game data, Discord-Minecraft account links, channels the Realms bot could read |
| Not affected | Account passwords, payment data and Premium Points |
| Response | Server cleaned twice and re-checked, important credentials changed, attacker reported |
| Contact | [email protected] |
About the Author
Sen
Founder, Owner, and Developer
Kaizen Network Contributor
 Join Discord